Identity attacks keep coming, and security teams still cannot follow every important sign-in event by reading logs by hand.
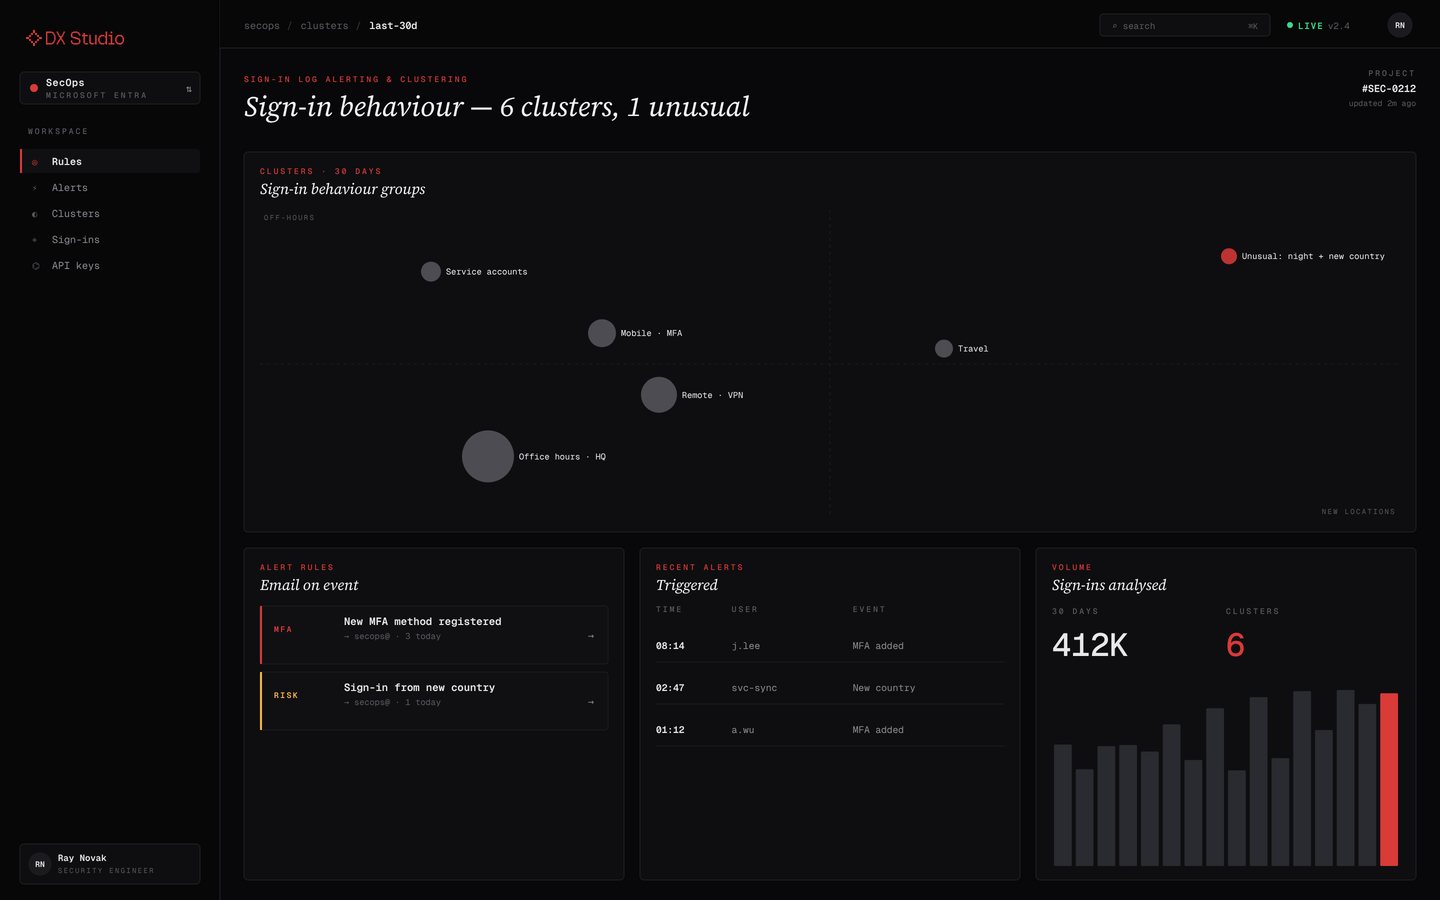
Security teams struggled to follow important identity events and unusual sign-in behaviour by reading logs by hand.
Authorised users define two kinds of commands: alert by email when a specific event happens (such as a new MFA method), and cluster past sign-ins into behaviour groups.
Key identity events surface automatically, and unusual patterns are easier to spot.
Need something like this?
Tell us what you are building. We reply with how we would approach it and a rough timeline.